Trustity Control Platform · TAO Agent
VisionX, GenGuard, FileGuard, Vault/PAM, and HostGuard are TCP capabilities - not standalone products - enforced by TAO where work happens. Need the portal on your own servers? TCP On-Prem.
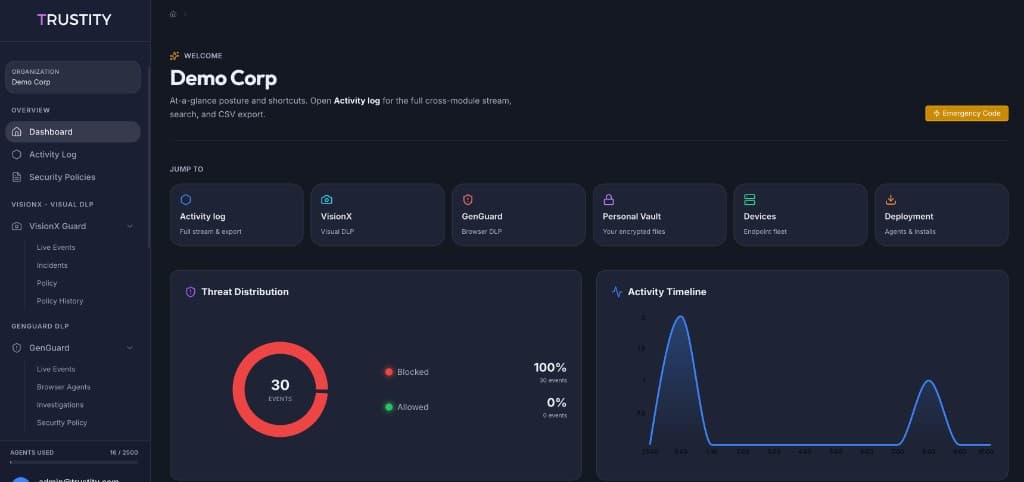
One agent runtime. The capabilities of Trustity Control Platform - not separate products parked side by side.
Visual DLP - detection, evidence, and lock on the interactive desktop.
Browser and workstation DLP under one TCP policy.
File labels and on-station discovery. Ransomware protection follows in 2027.
Secrets vault and local privileged password rotation.
Failed-logon detection, host blocks, portal alerts.
Traditional DLP misses phones, cameras, and lenses aimed at screens. VisionX detects visual-channel risks on the endpoint, reports evidence to the portal, and can lock the workstation until an admin unlock code is entered.
GenGuard with TAO protects the browser; GenGuard inside TAO protects the workstation. Block sensitive pastes and file transfers, enforce domains, and surface Shadow IT from one portal policy.
The file stays on the station. TAO remembers a fingerprint, GenGuard refuses it in the browser, and discovery proposes a label when the content is obviously sensitive. VisionX still watches the screen, Vault still holds the credential, and HostGuard still watches the sign-in. FileGuard is how those controls learn which file matters.
* Ransomware protection is scheduled for the first quarter of 2027. Classification, discovery, and browser enforcement are available now.
Explore FileGuardEncrypt work files in Personal and organization File Vault with a user PIN Trustity does not hold, and rotate local admin credentials on a schedule. From a station, an operator can also disable a local account or issue a temporary local user for a limited time. TAO applies the change on the endpoint and reports it to the portal for authorized operator workflows. On Linux, the same actions lock or create a local account; an administrator there is root or a member of sudo, wheel, or admin.
Catch brute-force attempts on the host. TAO watches failed logons, creates firewall rules for offending IPs, and reports incidents to the Cloud Portal.
Protect SMB file traffic and DNS at the network edge - inline reverse proxy, policy-driven DNS nodes, and offline-ready operation. A Trustity portfolio product, sold and licensed separately from the Cloud Portal.
Portfolio layer
TAO secures the endpoint. Axiom secures the protocols clients already use for files and DNS - without requiring software on every workstation for that path.
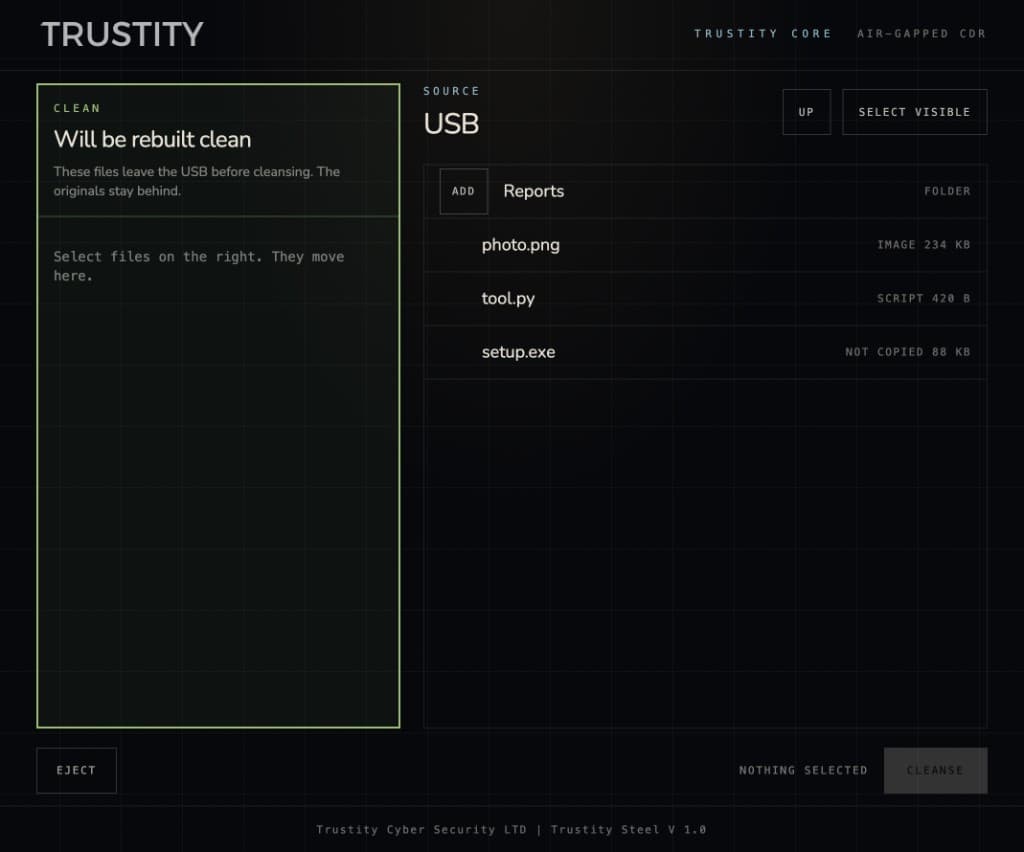
Axiom documentation →Customer portal ↗Move files across an air gap. Element is software: run it on a kiosk, or on a computer that stays on. It rebuilds each selected file in its original format. Clean files leave with a scan report. A file can also travel sealed to that machine, encrypted with its TPM.
Practical controls for hybrid workstations and servers.
TAO unified agent - Windows service + session helper; Linux server modules.
Policy, vault, agents, critical alerts, retention, and Security Assurance readiness.
Deploy the controls your environment needs - activate capabilities without fragmenting your stack.
SIEM / syslog, alert routing, and operational workflows from the portal.
Windows endpoints (full suite). Linux servers (PAM, IPS, inventory).
Asset inventory reporting from TAO into the portal.
Read the domain the organization already has. See which computers have TAO, and optionally apply VisionX, GenGuard, ZeroDevice, and HostGuard by computer group. The portal does not change the directory.
See our Trust Center and Privacy Policy for data handling.
Scoped, revocable keys from the Cloud Portal for read-only org, agent, alert, and audit queries. License keys are not API credentials. API reference
Password + MFA today; SSO domain discovery/start and SCIM Users lifecycle provisioning in preview. Session controls for operators.
Owners and Admins can enforce MFA for privileged portal roles, switch between authorized organizations, stage IdP metadata, provision and suspend users through SCIM, route deduplicated critical alerts, manage append-only audit retention (archive mode - not a tamper-evident GA claim), roll out TAO through deployment rings, and track measured Security Assurance readiness - without claiming a completed SOC 2 certification.
Deployment
Copy the organization key, download the current TAO build, and enroll endpoints. The same Cloud Portal then shows heartbeat, inventory, and PAM status.
Open Cloud Portal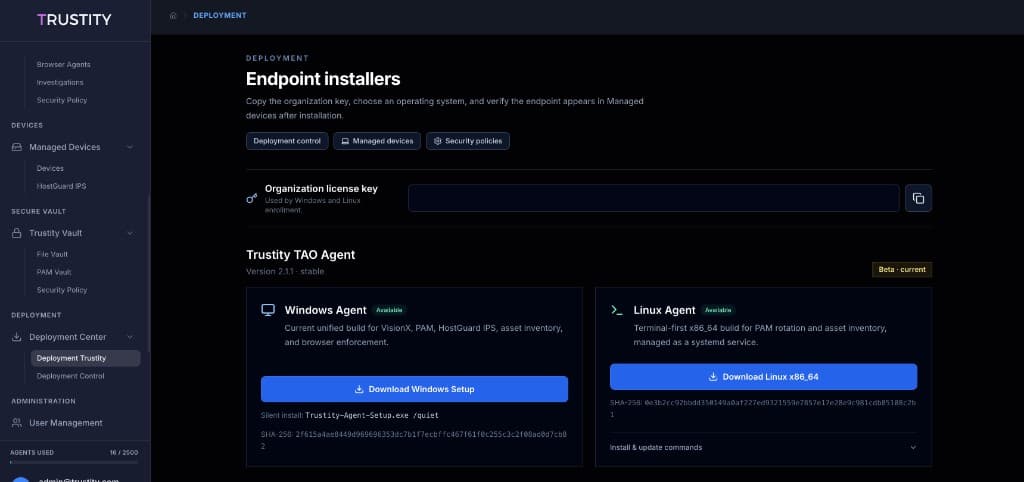
Start in the Trustity Cloud Portal - then install the agent and enable your modules.